
Learn Ethical Hacking, Cybersecurity, and Penetration Testing
Ethical hacking is an important part of modern cybersecurity practices.
It helps organizations identify security weaknesses before malicious attackers exploit them.
Moreover, ethical hacking uses authorized techniques to evaluate digital security.
Therefore, businesses increasingly need professionals with strong offensive security skills.
Modern organizations depend heavily on applications, networks, and cloud platforms.
Consequently, these environments require continuous security assessment and monitoring.
Ethical hacking provides a proactive approach for discovering potential vulnerabilities.
For aspiring technology professionals, this field offers several career opportunities.
Furthermore, security skills are valuable across many technology-driven industries.
Learning ethical hacking can therefore support a career in cybersecurity.
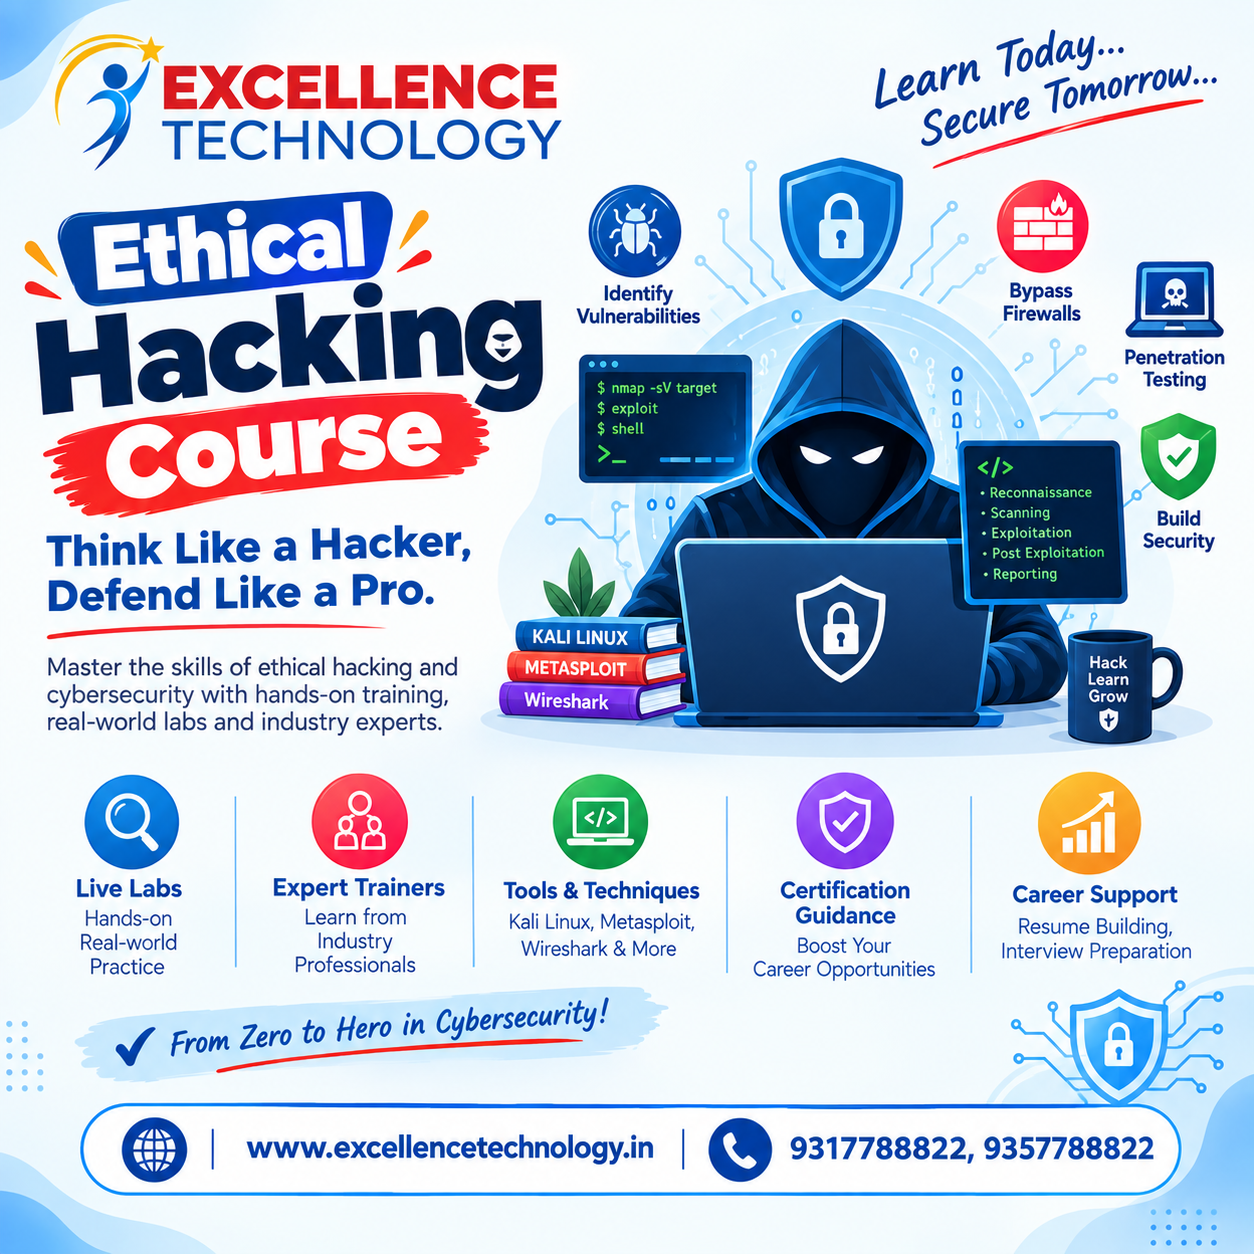
What Is Ethical Hacking?
Ethical hacking involves authorized security testing of computer systems.
Security professionals identify vulnerabilities using controlled and approved techniques.
The purpose is to improve security rather than cause damage.
Therefore, ethical hackers operate within clearly defined legal boundaries.
Organizations provide permission before security testing begins.
They may also define specific systems, applications, and testing limitations.
Ethical hackers then examine these environments for potential weaknesses.
They document their findings and provide recommendations for improving security.
The practice is also known as penetration testing or authorized security testing.
However, ethical hacking can involve broader activities than penetration testing.
Why Is Ethical Hacking Important?
Cyber threats continue evolving as organizations adopt new technologies.
Therefore, businesses need proactive methods for identifying security weaknesses.
Attackers may target applications, networks, accounts, cloud infrastructure, or endpoints.
A single vulnerability can potentially expose sensitive organizational information.
Ethical hacking helps organizations discover weaknesses before malicious exploitation occurs.
Security teams can then prioritize vulnerabilities according to their potential impact.
Furthermore, regular security assessments can support stronger security practices.
They can also provide valuable insights into existing security controls.
Consequently, organizations can improve their security posture through authorized testing.
How Ethical Hacking Works
An ethical hacking engagement generally follows a structured methodology.
The exact process depends on the organization's goals and authorization.
- Planning and Authorization Security professionals first define the testing scope and objectives. They identify systems that can legally undergo security testing. Authorization is essential before any testing activity begins. Therefore, written permission helps establish clear testing boundaries.
- Reconnaissance Ethical hackers collect relevant information about approved target environments. This stage helps professionals understand the available attack surface. Information may include domains, applications, technologies, and network details. However, all activities must remain within the approved scope.
- Vulnerability Identification Professionals analyze systems for potential security weaknesses. They may use scanners alongside manual security assessment techniques. The objective involves identifying vulnerabilities that could create security risks.
- Controlled Security Testing Ethical hackers carefully validate identified vulnerabilities. Testing should avoid unnecessary disruption or damage to systems. Professionals use controlled techniques to confirm security weaknesses.
- Analysis Security specialists analyze the potential impact of identified vulnerabilities. They determine which weaknesses require greater attention.
- Reporting Professionals document vulnerabilities, evidence, and recommended remediation steps. Reports help organizations understand and address identified security weaknesses.
- Remediation and Retesting Organizations address vulnerabilities based on security recommendations. Ethical hackers may then conduct authorized retesting afterward. This confirms whether previously identified weaknesses have been resolved.
Ethical Hacking vs Malicious Hacking
The primary difference involves authorization, purpose, and legal boundaries.
Ethical hackers receive permission before evaluating systems or applications.
Their objective is to identify weaknesses and improve organizational security.
Malicious hackers operate without authorization and may seek personal benefits.
They can steal information, disrupt services, or compromise digital systems.
Therefore, authorization is a fundamental distinction between these activities.
Ethical security professionals must follow defined rules during every engagement.
They must also protect sensitive information discovered during testing.
Types of Ethical Hacking
Organizations may conduct different types of authorized security assessments.
Each assessment focuses on specific technology environments or security objectives.
Network Security Testing
Network testing evaluates infrastructure for potential security weaknesses.
Professionals examine network configurations, services, and security controls.
Web Application Testing
Web application testing focuses on application-level security vulnerabilities.
Testers evaluate approved applications for weaknesses affecting users or data.
Mobile Application Testing
Mobile security testing evaluates applications designed for mobile devices.
Professionals examine authentication, data handling, and application behavior.
Wireless Security Testing
Wireless testing evaluates authorized wireless networks and configurations.
It can help identify weaknesses within wireless security controls.
Cloud Security Testing
Cloud assessments examine approved cloud environments and configurations.
They help identify potential risks across cloud-based infrastructure.
Social Engineering Assessments
Authorized social engineering assessments evaluate organizational security awareness.
They may test whether employees recognize simulated security threats.
Such activities require explicit authorization and carefully defined boundaries.
Common Ethical Hacking Methodologies
Security professionals use structured frameworks during authorized assessments.
These methodologies help ensure testing remains organized and consistent.
Black Box Testing
Black box testing provides limited information about the target environment.
The approach simulates an external attacker with minimal prior knowledge.
White Box Testing
White box testing provides extensive information about the target environment.
Testers may receive architecture, source code, or configuration information.
Gray Box Testing
Gray box testing provides partial information to security professionals.
It combines characteristics of black box and white box approaches.
Therefore, organizations can select approaches according to their security objectives.
Essential Ethical Hacking Skills
A successful career requires strong technical and analytical capabilities.
Therefore, learners should develop several important ethical hacking skills.
Networking
Networking knowledge provides a foundation for cybersecurity professionals.
Students should understand protocols, ports, routing, and network architecture.
Operating Systems
Security professionals frequently work with Linux and Windows environments.
Therefore, operating system knowledge remains essential for security testing.
Programming
Programming helps professionals understand software behavior and vulnerabilities.
Python, JavaScript, and scripting languages can support security automation.
Web Technologies
Ethical hackers should understand how modern web applications operate.
Knowledge of HTTP, APIs, databases, and authentication is valuable.
Cybersecurity Fundamentals
Students should understand common vulnerabilities, threats, and security controls.
These concepts provide essential context for security assessment activities.
Security Tools
Professionals use specialized tools during authorized security assessments.
However, understanding concepts remains more important than memorizing tools.
Analytical Thinking
Security testing requires careful analysis of application and system behavior.
Professionals must identify relationships between vulnerabilities and potential risks.
**
Popular Ethical Hacking Tools**
Security professionals use different tools for authorized testing.
The appropriate tool depends on the assessment scope and objectives.
Nmap
Nmap helps professionals understand network services within authorized environments.
It can provide useful information about networked systems and services.
Burp Suite
Burp Suite supports web application security testing and analysis.
It helps security professionals examine approved web application traffic.
Wireshark
Wireshark analyzes network traffic for troubleshooting and security investigations.
It can help professionals understand communication between networked systems.
Metasploit
Metasploit provides a framework for authorized security research and testing.
Professionals use it within controlled environments to validate vulnerabilities.
OWASP ZAP
OWASP ZAP supports web application security testing activities.
It can help identify potential vulnerabilities within authorized applications.
Kali Linux
Kali Linux provides numerous tools for security research and testing.
It is widely used within controlled cybersecurity learning environments.
Benefits of Ethical Hacking
Organizations can gain several benefits from authorized security testing.
First, it helps identify vulnerabilities before attackers discover them.
Second, security testing provides practical insights into existing security controls.
Third, it can support better vulnerability management and remediation.
Furthermore, assessments can help organizations understand potential attack paths.
This information can improve defensive strategies and security planning.
Ethical hacking can also support security awareness across technical teams.
Security findings provide useful lessons for developers and administrators.
Therefore, authorized testing can strengthen an organization's overall security approach.
Ethical Hacking and Cybersecurity
Ethical hacking represents one important component of broader cybersecurity.
Cybersecurity includes prevention, detection, response, recovery, and security governance.
Ethical hackers primarily focus on discovering weaknesses through authorized assessments.
Security teams then use those findings to improve defensive controls.
Therefore, ethical hackers often collaborate with security engineers and analysts.
Their combined efforts can create stronger organizational security practices.
Ethical Hacking and Penetration Testing
Penetration testing is closely associated with ethical hacking.
However, the terms are not always completely interchangeable.
Penetration testing usually involves controlled attempts to validate vulnerabilities.
Ethical hacking can include broader security assessment activities.
For example, an engagement may include vulnerability analysis and security reviews.
It may also include controlled social engineering assessments.
Therefore, penetration testing can be considered one part of ethical hacking.
Ethical Hacking Certifications
Certifications can help learners demonstrate cybersecurity knowledge.
Several certification pathways focus on security fundamentals and penetration testing.
However, certification alone does not guarantee professional readiness.
Practical experience remains essential for developing effective security skills.
Students should therefore combine certification preparation with laboratory practice.
Controlled environments provide opportunities to apply concepts safely.
Capture-the-flag challenges can also strengthen problem-solving abilities.
Additionally, security projects can demonstrate practical knowledge to employers.
Career Opportunities in Ethical Hacking
Growing cybersecurity requirements create several professional opportunities.
Therefore, learners can explore different roles within information security.
Ethical Hacker
Ethical hackers perform authorized security assessments for organizations.
They identify vulnerabilities and provide recommendations for improving security.
Penetration Tester
Penetration testers conduct controlled security assessments of approved systems.
They document vulnerabilities and help organizations understand potential risks.
Security Analyst
Security analysts monitor systems and investigate suspicious activities.
They may use assessment findings to strengthen defensive controls.
Vulnerability Analyst
Vulnerability analysts identify, prioritize, and track security weaknesses.
They help organizations manage vulnerabilities across technology environments.
Security Consultant
Security consultants advise organizations about cybersecurity risks and controls.
They may conduct assessments and recommend appropriate security improvements.
Application Security Engineer
Application security engineers help integrate security throughout software development.
They assess applications and support secure development practices.
Ethical Hacking Course: What Should You Learn?
A structured ethical hacking course can provide organized cybersecurity training.
However, learners should evaluate course content carefully before enrolling.
A comprehensive program should cover networking and operating system fundamentals.
It should also introduce web applications and cybersecurity concepts.
Students should learn vulnerability assessment and penetration testing methodologies.
They should practice within legally authorized laboratory environments.
A strong course should also include practical projects.
Projects allow learners to apply concepts within controlled scenarios.
Furthermore, trainers should emphasize legal and ethical responsibilities.
Students must understand authorization before conducting any security assessment.
Ethical Hacking Best Practices
Responsible security testing requires careful planning and professional discipline.
First, obtain explicit authorization before conducting any assessment.
Second, define the testing scope and permitted activities clearly.
Third, protect sensitive information discovered during the assessment.
Furthermore, avoid unnecessary disruption to business-critical systems.
Testing should follow agreed rules and communication procedures.
Finally, provide clear reports with practical remediation recommendations.
These practices help organizations gain value from security assessments.
Legal and Ethical Responsibilities
Ethical hacking must always operate within legal authorization.
Testing systems without permission can create serious legal consequences.
Professionals should therefore obtain documented authorization before testing.
They should also understand applicable organizational and legal requirements.
Responsible security professionals respect privacy and data protection requirements.
They avoid accessing information beyond the approved testing scope.
Therefore, technical skills must always accompany professional responsibility.
Future of Ethical Hacking
Technology continues changing the cybersecurity landscape rapidly.
Consequently, ethical hackers must continuously develop their technical knowledge.
Cloud computing creates new environments requiring specialized security assessments.
Similarly, connected devices create additional security considerations.
Artificial intelligence may also influence security assessment and defense.
Security professionals will need to understand emerging technologies carefully.
Application security will remain important as software becomes increasingly interconnected.
Furthermore, organizations will continue requiring proactive security assessments.
Therefore, the future requires adaptable and continuously learning security professionals.
How to Start an Ethical Hacking Career
Starting an ethical hacking career requires strong cybersecurity fundamentals.
First, learn networking, Linux, Windows, and basic programming concepts.
Next, understand web applications, databases, APIs, and authentication systems.
Then, study common vulnerabilities and defensive security practices.
Afterward, practice security testing inside authorized laboratory environments.
Platforms designed for cybersecurity education can provide useful practice opportunities.
Build projects demonstrating vulnerability identification and security reporting skills.
Additionally, consider certifications aligned with your career goals.
Finally, develop strong communication skills for professional security reporting.
Technical findings become valuable when organizations can understand and address them.
Why Choose an Ethical Hacking Course?
A structured ethical hacking course can provide guided cybersecurity learning.
It can organize complex concepts into manageable learning stages.
Students can learn networking, security testing, vulnerability assessment, and reporting.
They can also practice using industry-relevant security tools safely.
Furthermore, project-based training can improve practical problem-solving abilities.
Career-focused programs may also provide interview and resume preparation.
Before enrolling, review the curriculum and practical laboratory components.
Also, evaluate trainer experience and project-based learning opportunities.
Choose training that emphasizes both technical skills and ethical responsibility.
Conclusion
Ethical hacking helps organizations identify security weaknesses through authorized testing.
It supports proactive cybersecurity and better vulnerability management practices.
Modern security professionals need networking, programming, cloud, and application knowledge.
They also require strong analytical thinking and responsible testing practices.
The cybersecurity industry continues evolving with new technologies and threats.
Therefore, professionals must continue learning throughout their careers.
For aspiring security professionals, ethical hacking offers several career opportunities.
With structured training and practical experience, learners can build valuable skills.
Ready to Start Your Ethical Hacking Career?
Enroll in a professional ethical hacking course and develop practical cybersecurity skills.
Learn security fundamentals, vulnerability assessment, penetration testing, and security reporting.
Practice safely within authorized labs while building a strong technical portfolio.
Start your ethical hacking journey today and prepare for the future of cybersecurity!


Top comments (0)